AI-AIDED CYBERSECURITY COURSE
TUESDAYS & THURSDAYS
5 PM PST / 8 PM EST
AI-AIDED CYBERSECURITY
8 OCT 2026 - 3 DEC 2026
DURATION:
9 WEEKS
TUESDAYS & THURSDAYS
5 PM PST / 8 PM EST
Strengthen digital defenses with AI. Learn how AI is used to attack and protect systems, enhance threat detection, and boost security efficiency — all while upholding ethical standards.
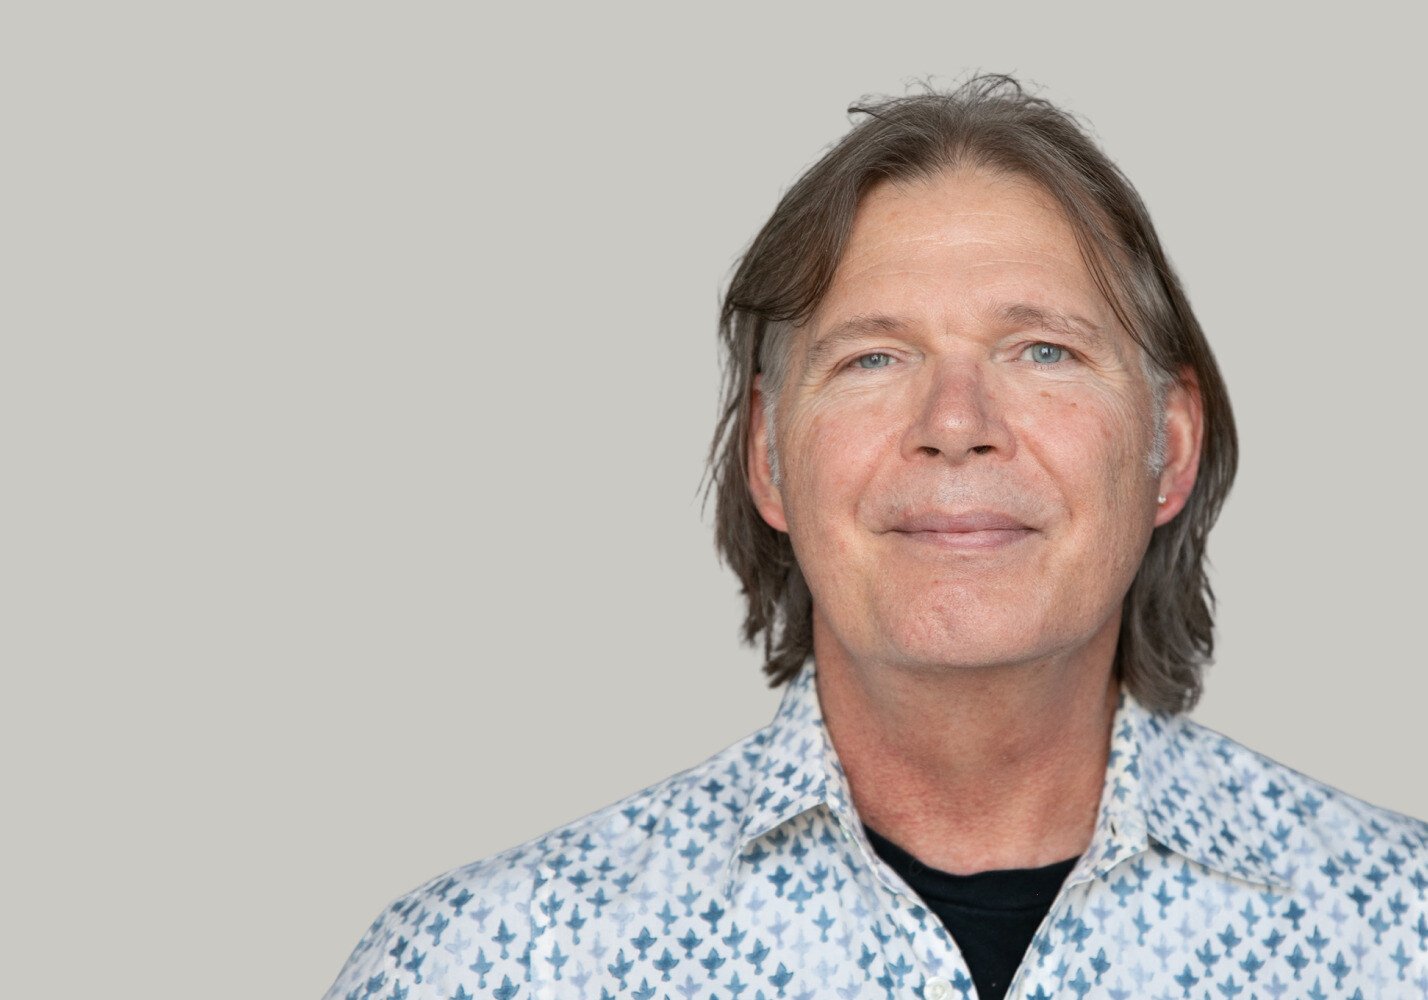
Stephen Smith is a security veteran with a proven track record. He’s worked with Amazon, Google, HP, and the US Navy, and will teach you how to upgrade your cybersecurity strategies.
THIS COURSE IS FOR YOU, IF...
-
YOU ARE A CYBERSECURITY ANALYST READY TO LEVEL UP
Take the guesswork out of AI-powered security. Learn AI/ML techniques to detect anomalies, automate threat responses, and stay ahead of cybercriminals.
-
YOU ARE A SYSTEM OR NETWORK SECURITY ENGINEER
Struggling to integrate AI into your security workflow? Master AI-driven behavioral analysis to detect insider threats, analyze system behavior, and safeguard your networks.
-
YOU ARE A SECURITY MANAGER OR RISK ASSESSOR
AI is changing risk management — are you keeping up? Learn how to integrate AI/ML into your security strategy while navigating ethical and regulatory challenges.
-
YOU ARE A SYSTEM OR CLOUD ADMINISTRATOR
Cloud security needs more than traditional defenses. Apply AI/ML to detect cloud threats, automate incident responses, and fortify your organization’s security posture.
Our students work in 1600+ companies worldwide
Dive into real-world cybersecurity challenges and sharpen your threat detection skills. Investigate three embedded incidents inside a simulated financial-sector SOC, explore defense strategies, and apply AI-driven solutions to detect anomalies, mitigate risks, and strengthen security systems.
In 16 hands-on labs, sharpen your security AI skills, train intrusion detection models, build anomaly detectors, extract threat intel with NLP, and build a security-triage agent using Python, Scikit-learn, and LangGraph.
Turn theory into practice and refine your cyber expertise. Your final capstone project focuses on Malware Detection with ML, where you'll streamline data collection, preprocess datasets, engineer features, and train models to detect malicious activity.
STEPHEN SMITH
LINKEDIN PROFILE- Serves as Principal Security Architect in Microsoft's Cyber Defense Organization, leading response for high-profile security incidents
- Held Incident Data Analysis Lead for the CISO at Google Cloud, then Senior Technical Program Manager at Amazon's Project Kuiper
- Brings over 40 years of threat hunting and adversary-detection experience, starting as a US Navy submarine missile technician
- Experienced Network Architect, and Engineering Director with security leadership role experience at Microsoft and HP, specializing in high-profile incident response
Get oriented with the course, meet your instructor, and preview what's ahead before opening the floor to questions.
- Instructor introduction
- Course structure and assignments
- Q&A
Orient yourself to the current AI-security landscape, using the ML lifecycle as your course framework, and see how LLM-powered attacks like polymorphic malware and AI-assisted phishing are entering the wild.
- ML lifecycle as course framework
- Taxonomy of AI security applications
- LLM-powered attacks in the wild
- Prompt fundamentals and context management
- Course toolchain: Python, LangChain, Copilot
- Lab: Environment setup and first LLM API call for security log summarization
Assignment A1: Onboarding & Baseline (part 1 of 2)
Toolchain setup plus initial exploratory data analysis on the OpCenter dataset; combines with the Lesson 02 baseline classifier into one graded deliverable due before Lesson 03.
Build the supervised, unsupervised, and reinforcement learning foundation you'll need for the rest of the course, grounded entirely in security data and its evaluation metrics.
- Supervised, unsupervised, and reinforcement learning
- Bias-variance tradeoff in security models
- Evaluation metrics: precision, recall, F1, AUC-ROC
- Dataset shift and model decay
- Scikit-learn workflow with security data
- Lab: Exploratory data analysis and a first classifier trained on network-flow data
Assignment A1: Onboarding & Baseline (complete)
Lesson 01 setup and EDA plus a trained, evaluated baseline classifier on OpCenter alerts. Due before Lesson 03. (15 pts)
Master the data-preparation skills that make or break security ML models, from sparse labels and class imbalance to reproducible, versioned pipelines.
- Characteristics of security data
- Data collection and pipeline design
- Class-imbalance strategies: SMOTE, cost-sensitive learning
- Data versioning and reproducibility
- Using LLMs to generate preprocessing code
- Lab: Ingest and normalize all four OpCenter sources into a data characterization report
Assignment A2: Detection Foundation (part 1 of 2)
Data pipeline (Capstone Module 1) built from the Lesson 03 lab; combines with the Lesson 05 detection and anomaly layer into one graded deliverable due before Lesson 06.
Apply supervised ML to threat detection through the full build-evaluate-tune loop, from feature engineering to threshold tuning for operator cost asymmetry.
- Threat detection as classification
- Feature engineering for security
- Model selection: trees, forests, boosting
- Threshold tuning for cost asymmetry
- Explainability: SHAP values for analyst trust
- Lab: Build a supervised IDS classifier on the OpCenter feature table and generate a SHAP explanation
Apply unsupervised anomaly detection where labeled threat data is unavailable or stale, combining Isolation Forest and Autoencoder approaches into a hybrid pipeline.
- Point, contextual, and collective anomalies
- Isolation Forest, Local Outlier Factor, Autoencoders
- Baseline establishment and drift detection
- Hybrid supervised/unsupervised pipelines
- Lab: Add an anomaly-detection layer and build an LLM triage-summary prompt
Assignment A2: Detection Foundation (complete)
Lesson 03 data pipeline plus the Lesson 04–05 detection and anomaly layer, with an LLM triage summary. Due before Lesson 06. (30 pts)
Develop the ML literacy to understand what EDR tools do under the hood, judge when to trust their verdicts, and build supplemental detection for the gaps they leave.
- EDR as an ML system
- Tabular ML on static PE features
- Model explainability: SHAP for SOC alerts
- False-negative analysis and coverage gaps
- Evasion from a defender's perspective
- Lab: Replicate an EDR scoring pipeline on EMBER2024 and apply SHAP to high-severity verdicts
Develop advanced feature engineering for security data and build the visualization fluency needed for model interpretation and stakeholder communication.
- Domain-informed feature construction
- Dimensionality reduction: PCA and UMAP
- Feature selection techniques
- Interactive dashboards: Plotly and Streamlit
- Lab: Engineer a domain-informed feature set and build an interactive Streamlit dashboard
Assignment A3: Enrichment & Interpretation (part 1 of 2)
Feature engineering and dashboard (Capstone Module 3) built from the Lesson 07 lab; combines with the Lesson 09 behavioral scorer and Lesson 10 threat-intel enrichment into one graded deliverable due before Lesson 11.
Apply AI to two high-ROI workflows: automated vulnerability prioritization and AI-assisted incident investigation, from CVE triage to LLM-generated incident narratives.
- Vulnerability prioritization beyond CVSS
- ML for CVE triage
- AI-assisted incident timeline reconstruction
- Copilot for Security and similar tools
- Lab: Build a CVE-prioritization model and generate an incident narrative from an alert timeline
Build UEBA systems that detect insider threats, compromised accounts, and abnormal lateral movement using behavioral baselines and peer-group comparison.
- UEBA architecture: baselining, scoring, alerting
- Behavioral features and peer-group comparison
- Sequence modeling: Hidden Markov Models, LSTMs
- Identity-centric detection: Entra ID telemetry
- Lab: Build a user-behavior baseline and anomaly scorer on the OpCenter Entra ID stream
Apply NLP and LLMs to the security text domain, from threat-intel extraction to RAG-grounded knowledge bases and the prompt-injection risks they introduce.
- Security NLP landscape
- Transformer-based embeddings for classification
- RAG for security knowledge bases
- Prompt injection and data-poisoning risks
- Lab: Build an NLP extraction pipeline against the OpCenter CTI corpus
Assignment A3: Enrichment & Interpretation (complete)
Lesson 07 feature engineering and dashboard, the Lesson 09 behavioral scorer, and the Lesson 10 CTI extraction and alert-enrichment pipeline. Due before Lesson 11. (30 pts)
Apply AI to network traffic analysis and cloud workload protection, integrating modern cloud-native telemetry with Microsoft Sentinel as the primary example.
- Network traffic classification and flow-based ML
- DDoS detection and mitigation
- Cloud security telemetry: CSPM, CloudTrail
- Integrating detections into SIEM/SOAR
- Lab: Network-flow classification on OpCenter NetFlow and a Sentinel KQL query from LLM-generated logic
Understand the full adversarial ML threat surface, from feature-space evasion to model extraction, and build the assessment skills to evaluate your own systems.
- Adversarial ML taxonomy
- Evasion: feature-space vs. problem-space
- Poisoning attacks and backdoors
- LLM-specific attacks: prompt injection, jailbreaking
- Lab: Craft a feature-space evasion sample against the EMBER2024-trained classifier from Lesson 06
Build practical defensive skills for hardening ML-based security systems against the attacks covered in Lesson 12, from adversarial training to drift monitoring.
- Adversarial training and input validation
- Model robustness evaluation and red-teaming
- LLM guardrails and output filtering
- Monitoring deployed models for drift
- Lab: Craft evasion samples against the capstone classifier and implement adversarial training
Assignment A4: Capstone Final (part 1 of 2)
Adversarial evaluation and hardening (Capstone Module 5) built from the Lesson 13 lab; combines with the Lesson 15 governance memo and Lesson 16 integration and presentation into the final graded deliverable due after Lesson 16.
Understand agentic AI systems end to end — how to build them, how to secure them, and how adversaries weaponize them for offense.
- Agentic architecture: LLMs, tools, orchestration
- Security automation: triage pipelines, IR co-pilots
- MCP for security tooling
- Securing agentic systems: privilege minimization
- Lab: Build a security-triage agent with LangGraph on OpCenter alerts
Develop the governance and ethics literacy practitioners need to deploy AI security systems responsibly and navigate emerging regulation like the EU AI Act.
- Bias and fairness in security AI
- AI governance: NIST AI RMF, EU AI Act
- Data governance: retention, consent, cross-border transfer
- Accountability for the model, alert, and miss
- Lab: Audit a trained model for bias and document findings in a governance memo
Synthesize the course through operational AI-security deployment and demonstrate mastery through your capstone presentation and peer review.
- End-to-end ML lifecycle review
- Deploying security ML: MLOps, SIEM/SOAR
- The AI-augmented SOC: human-AI teaming
- Future vectors: multimodal and foundation models
- Lab: Demo the AI-augmented SOC system, live-demonstrate detection of an embedded incident, and present a deployment plan
Assignment A4: Capstone Final — AI-Augmented SOC System (complete)
Lesson 13 adversarial evaluation and hardening, the Lesson 15 bias audit and governance memo, plus the integrated system, live incident demonstration, and deployment plan.
What our students say
"I really enjoy the format of the course. Lectures with real life examples and an ongoing case study. Also built in 20 minutes at the end of each class for questions is helpful."
"Overall I'm impressed with the level of detail and explanation around particular topics and subjects. There's a real depth to each module which for learning allows the information to stay in your brain."
"The group activities, they allow us to interact and exchange ideas, plus the way it is structured is challenging and mind twisting as we collaborate in different parts of the ideation."
"I enjoyed the structure of the class. I like how we learned about a topic and practiced it in the workshops. It’s helped me to apply what I learned!"